☎ Call Today
Criminal Defense • Frisco, Texas
Serving 9 DFW Counties — Collin • Dallas • Denton • Tarrant • Rockwall • Kaufman • Ellis • Johnson • Hunt — Available 24/7
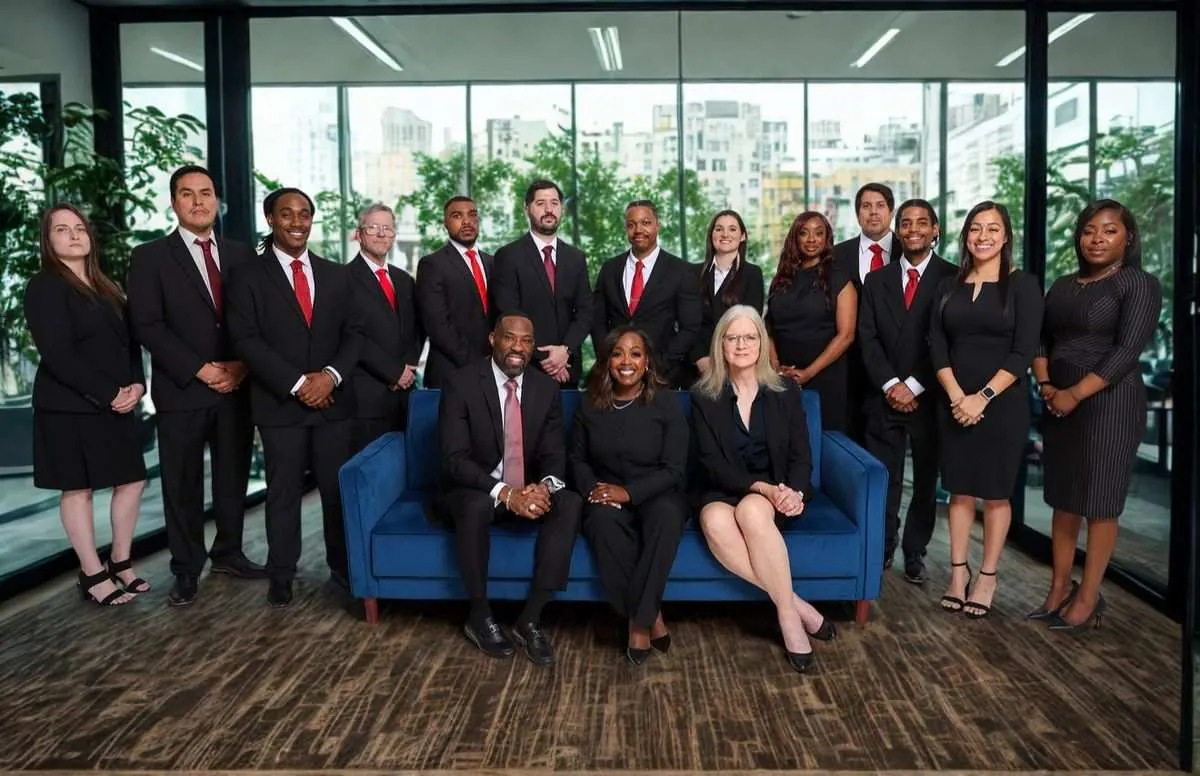
The L and L Law Group team at our Frisco, Texas office — co-founding partners Reggie London and Njeri London with staff
Our Frisco office●Est. 2011
The L and L Law Group team·Frisco, Texas
White Collar & Fraud · Breach of Computer Security

Breach of Computer Security Defense — Texas Penal Code § 33.02

Breach of computer security under Texas Penal Code § 33.02 makes it a crime to knowingly access a computer, network, or system without the owner’s effective consent. The grade runs from a Class B misdemeanor up to a first-degree felony, driven by the aggregate-loss amount and a handful of enhancement triggers. L and L Law Group defends the consent fight and the loss-amount math across Collin, Dallas, Denton, and Tarrant Counties.

A Texas breach of computer security charge under Penal Code § 33.02 runs on two grading tracks. Simple knowing access without the owner’s effective consent under § 33.02(a) starts as a Class B misdemeanor, with built-in felony bumps for government or critical-infrastructure systems and for repeat offenders. Access carried out with intent to defraud or harm under § 33.02(b-1) is graded by the "aggregate amount" — the total dollar value involved — and can reach a first-degree felony. Most cases are not about hacking: they are about whether you had permission, whether you knew you did not, and how the State counted the loss. The "effective consent" definition under § 33.01(12) — and the knowing mental state that Muhammed and Farris attach to it — is the operative battleground in most contested § 33.02 cases in DFW county and district courts.

breach of computer security: Texas grade & punishment at a glance
Conduct / aggregate amountOffense levelConfinementMax fine
Knowing access without effective consent — § 33.02(a)Class B misdemeanorUp to 180 days, county jail$2,000
Government/critical-infrastructure system, or 2+ prior Ch. 33 convictions — § 33.02(b)State jail felony180 days – 2 years, state jail$10,000
Fraud/harm intent, $2,500 to under $30,000 — § 33.02(b-2)(4)State jail felony180 days – 2 years, state jail$10,000
$30,000 to under $150,000 — § 33.02(b-2)(5)Third-degree felony2 – 10 years, TDCJ$10,000
$150,000 to under $300,000; or ID info from one computer — § 33.02(b-2)(6)Second-degree felony2 – 20 years, TDCJ$10,000
$300,000+; or ID info from more than one computer — § 33.02(b-2)(7)First-degree felony5 – 99 years or life, TDCJ$10,000

Grade follows § 33.02 and the aggregate-amount bands in Tex. Penal Code § 33.02. Lower fraud-intent bands (under $2,500) run Class C through Class A misdemeanor; identity-information and government-system triggers raise the grade regardless of dollar amount.

13 min read 2,900 words Reviewed June 20, 2026 By Reggie London
Direct Answer

Breach of computer security under Texas Penal Code § 33.02 is the State’s general computer-intrusion offense: knowingly accessing a computer, computer network, or computer system without the owner’s effective consent. It is graded on two tracks. Simple access under § 33.02(a) is a Class B misdemeanor, with two built-in felony bumps — a state jail felony for a government or critical-infrastructure computer or for a defendant with two or more prior Chapter 33 convictions. Access with intent to defraud or harm under § 33.02(b-1) is graded by the aggregate amount under § 33.01(2) and runs from a Class C misdemeanor up to a first-degree felony, with identity-information and government-system triggers that raise the grade regardless of dollar amount. The decisive elements are “effective consent” under § 33.01(12) and the requirement — established in Muhammed v. State and applied in Farris v. State — that the State prove the defendant knew the access was unauthorized at the moment it occurred. Defense work attacks the consent scope, the knowledge proof, the aggregate-loss calculation, the device-search warrant under CCP art. 38.23, and the choice of state versus federal forum.

Free case review
Key Takeaways
  • Grade runs Class B misdemeanor to first-degree felony — simple access under § 33.02(a) is a Class B; fraud-or-harm intent is graded by aggregate amount under § 33.02(b-2).
  • Consent is the fight: “effective consent” under § 33.01(12) is stripped in five situations, including access used for a purpose other than the one it was given for — § 33.01(12)(E).
  • Knowledge wins cases — Muhammed v. State and Farris v. State require proof the defendant knew the access was unauthorized when it happened.
  • The loss number drives felony exposure — § 33.01(2) sweeps in investigation and data-restoration costs; auditing it line by line can drop the grade.
  • State or federal — the same conduct can be charged under § 33.02 and the federal CFAA, 18 U.S.C. § 1030; Van Buren narrows the federal statute but not Texas law.
Quick Case Review · 24/7

Get a free review

Direct to attorney — no call center. Most clients hear back within an hour.

By submitting, you agree to our Privacy Policy. No attorney-client relationship is formed until a written engagement is signed.

Texas Bar
Licensed since 2004
TXND · TXED
Federal Court Admitted
4.8 ★
Google Reviewed
9 DFW
Counties Served
24/7
Direct-to-Attorney Line
40+
Years Combined
Texas Bar Licensed TXND & TXED Federal 24/7 Jail Release Se Habla Español
Texas Legal Context

What the statute actually requires

Controlling statute Texas Penal Code § 33.02 (definitions at § 33.01)
Analytical framework Breach of computer security under Penal Code § 33.02 is graded on two tracks — a Class B misdemeanor base for knowing access without effective consent under § 33.02(a), and an aggregate-amount ladder up to a first-degree felony for access with intent to defraud or harm under § 33.02(b-1). The conduct line is low: "access" under § 33.01(1) reaches opening a folder, reading an email, or logging into a cloud account. The defining battles are "effective consent" under § 33.01(12), the knowing-it-was-unauthorized mental state under Muhammed v. State and Farris v. State, and the aggregate-loss calculation under § 33.01(2).
6 Texas-specific insights
  1. Consent — not access — decides these cases. "Access" under § 33.01(1) is satisfied by approaching, instructing, communicating with, storing data in, retrieving or intercepting data from, altering software in, or otherwise making use of any computer resource. No malware or password-cracking is required. Because the conduct line is so low, the contested element is almost always whether the owner gave effective consent and whether the defendant knew it was absent.
  2. § 33.01(12)(E) is the prosecutor’s favorite clause. Effective consent is stripped when it is "used for a purpose other than that for which the consent was given." A spouse given a password to pay bills who logs in to copy messages for a custody fight, or an employee allowed into a CRM who exports the whole client list on the way out, can be charged on this theory. The defense nails down exactly what the owner authorized, when, and for what — usually from emails, onboarding documents, and company policy.
  3. The knowledge element is where workplace cases are won. In Muhammed v. State, 331 S.W.3d 187, 192 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d), the court held the "knowing" mental state attaches to the consent, not just the act — the State must prove the defendant accessed the computer knowing the access was without the owner’s effective consent. Farris v. State, No. 10-21-00204-CR (Tex. App.—Waco Feb. 15, 2023, no pet.) (mem. op.), applied the rule to acquit where the accused had a reasonable basis to think access was permitted.
  4. The aggregate amount sets the felony grade. On the fraud-or-harm track, § 33.02(b-2) grades the offense by aggregate amount, and § 33.01(2) sweeps in the victim’s cost to investigate the intrusion and to restore, recover, or replace data — frequently a forensic-response invoice. Because that number sets the grade, auditing it line by line against the vendor invoices can drop a third-degree felony to a state jail felony or a misdemeanor.
  5. Identity-information and government-system triggers ignore dollar amount. Under § 33.02(b-2)(6)(C) and (7)(B), obtaining identifying information from one computer is a second-degree felony and from more than one computer a first-degree felony — regardless of dollar value. A zero-dollar intrusion touching personal data on two systems can be indicted at the same grade as a $300,000 fraud. Any fraud-or-harm access against a government or critical-infrastructure computer is at least a second-degree felony under (b-2)(6)(B).
  6. Texas law is broader than the federal CFAA after Van Buren. Van Buren v. United States, 593 U.S. 374 (2021), held that misusing access you are allowed to have is not a federal CFAA crime. Texas is written the other way: § 33.01(12)(E) strips consent used for an unauthorized purpose and § 33.02(b-1)(2) reaches policy violations paired with fraud intent. Conduct that survives Van Buren federally can still be charged under § 33.02 in a Texas courthouse.

What is breach of computer security under Texas law?

Breach of computer security is Texas’s general computer-intrusion crime. Under § 33.02(a), a person commits the offense by knowingly accessing a computer, computer network, or computer system without the effective consent of the owner. "Access" under § 33.01(1) is broad — no malware or password-cracking is required.

What surprises most clients is how little it takes to satisfy "access." The definition in § 33.01(1) reaches approaching, instructing, communicating with, storing data in, retrieving or intercepting data from, altering software in, or otherwise making use of any computer resource. Opening a folder, reading an email, running a database query, or logging into a cloud account all count. No malware, no password-cracking, no "hacking" in the Hollywood sense is required.

Because the conduct line is so low, the cases that get charged almost never look like cyberattacks. They look like a fired employee who downloaded a file over the weekend, a spouse who read text messages during a divorce, a business partner who pulled records off a shared server after a falling-out, or an IT contractor who went one step past the scope of work. In each of those, the access plainly happened. The defense is rarely "I didn’t touch it" — it is "I had permission" or "I didn’t know I didn’t." That is why the consent element, not the access element, is where these cases are decided.

Knowing access — § 33.02(a)
The accused must knowingly access a computer resource as § 33.01(1) defines it. An automated sync, a background app, or an accidental click is not knowing access. The "knowing" mental state is the starting point, and under Muhammed v. State it extends past the act to the absence of consent.
A computer, network, or system — § 33.01
The thing accessed must meet the § 33.01 definitions, which cover servers, laptops, phones, email and cloud accounts, point-of-sale terminals, and connected devices. The breadth of the definition means almost any digital device or account falls within the statute.
Without the owner’s effective consent — § 33.01(12)
No authorized person gave valid permission, or the permission failed one of the five § 33.01(12) tests. Consent is the heart of the offense and the most heavily contested element. Possessing valid credentials is not the same as having effective consent for the use actually made of them.
Knowledge that consent was absent
This is the element that wins cases. Texas courts have held the "knowing" mental state attaches to the consent, not just the act. In Muhammed v. State, 331 S.W.3d 187, 192 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d), the court held the State must prove the defendant knowingly accessed a computer knowing that the access was without the effective consent of the owner. A genuine, even mistaken, belief that access was allowed defeats the charge.

A § 33.02 case is rarely about whether a keystroke occurred — it is about authorization and the defendant’s state of mind. The State frequently overcharges by treating a departing employee’s file export, or a family member’s use of a shared password, as a felony intrusion when the consent picture is far murkier than the charging instrument suggests. Each of those is a fact-bound question, and each gives the defense room to argue for acquittal, charge reduction, declination, or a civil-side resolution.

The grade is not a footnote. The same conduct can be a fine-only Class C misdemeanor or a first-degree felony depending entirely on the number the State attaches to it and on whether identity information or a government system is involved. That is why the consent fight and the loss-amount audit run in parallel from the moment of retention.

What must the State prove?

For the base offense under § 33.02(a), the State must prove knowing access, a computer or network or system, the absence of the owner’s effective consent, and — critically — that the defendant knew consent was absent when the access happened.

For the base offense under § 33.02(a), the State must prove each element beyond a reasonable doubt:

1. Knowing access
The accused knowingly accessed a computer resource as § 33.01(1) defines it. An automated sync, a background app, or an accidental click is not knowing access.
2. A computer, network, or system
The thing accessed must meet the § 33.01 definitions, which cover servers, laptops, phones, email and cloud accounts, point-of-sale terminals, and connected devices.
3. Without the owner’s effective consent
No authorized person gave valid permission, or the permission failed one of the five § 33.01(12) tests above.
4. Knowledge that consent was absent
This is the element that wins cases. In Muhammed v. State, 331 S.W.3d 187, 192 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d), the court held the State must prove the defendant "knowingly accessed a computer… knowing that this act was without the effective consent of the owner." A genuine, even mistaken, belief that access was allowed defeats the charge.

The Tenth Court of Appeals reaffirmed and applied that rule in Farris v. State, No. 10-21-00204-CR (Tex. App.—Waco Feb. 15, 2023, no pet.) (mem. op.). Quoting the controlling line of authority, the court explained that "what makes accessing a computer unlawful under section 33.02(a) is that when the access occurs, the circumstances exist that the actor knows it is without the owner’s consent." On the facts, a person who accessed an SD card he found under his own desk — to figure out whose it was, believing it might be his — had not violated § 33.02, because there was no evidence he knew he lacked the owner’s consent. Farris is a clean illustration of the mistaken-authority defense: when the accused had a reasonable basis to think the access was permitted, the knowledge element fails.

A felony case under § 33.02(b-1) layers more on top: the specific intent to defraud or harm another, or to alter, damage, or delete property — and, on the policy-violation branch of § 33.02(b-1)(2), proof of a clear and conspicuous prohibition or an express contractual agreement plus intent to obtain or use data to carry out the fraud or harm. Every added element is one more thing the State can fail to prove.

What are the penalties under § 33.02?

Section 33.02 runs on two grading tracks. Simple access under subsection (a) starts as a Class B misdemeanor with two felony bumps. Fraud-or-harm cases under subsection (b-1) are graded by "aggregate amount" — the total dollar value — on the same value bands Texas uses for theft, up to a first-degree felony.

Section 33.02 runs on two grading tracks. Simple access under subsection (a) starts as a Class B misdemeanor with two built-in felony bumps. Fraud-or-harm cases under subsection (b-1) are graded by "aggregate amount" — the total dollar value involved — on the same value bands Texas uses for theft. The table below maps the full ladder; the takeaway for anyone facing a charge is that the same keystrokes can be a fine-only offense or a first-degree felony depending entirely on the number the State attaches to them.

ConductClassificationConfinementMax fine
Knowing access without effective consent — § 33.02(a)Class B misdemeanorUp to 180 days, county jail$2,000
Subsection (a) access against a government/critical-infrastructure computer, or with two or more prior Chapter 33 convictions — § 33.02(b)State jail felony180 days–2 years, state jail$10,000
Fraud/harm intent, aggregate amount under $100 — § 33.02(b-2)(1)Class C misdemeanorNone (fine only)$500
$100 to under $750 — § 33.02(b-2)(2)Class B misdemeanorUp to 180 days, county jail$2,000
$750 to under $2,500 — § 33.02(b-2)(3)Class A misdemeanorUp to 1 year, county jail$4,000
$2,500 to under $30,000 — § 33.02(b-2)(4)State jail felony180 days–2 years, state jail$10,000
$30,000 to under $150,000 — § 33.02(b-2)(5)Third-degree felony2–10 years, TDCJ$10,000
$150,000 to under $300,000; any amount against a government/critical-infrastructure system; or identifying information from one computer — § 33.02(b-2)(6)Second-degree felony2–20 years, TDCJ$10,000
$300,000 or more; or identifying information from more than one computer — § 33.02(b-2)(7)First-degree felony5–99 years or life, TDCJ$10,000

Two grading traps drive most of the felony exposure we see. The identity-information bumps in § 33.02(b-2)(6)(C) and (7)(B) make the offense a second-degree felony when identifying information is obtained from one computer and a first-degree felony when it comes from more than one — regardless of dollar amount. A zero-dollar intrusion that touches personal data on two systems can be indicted at the same grade as a $300,000 fraud. The ownership bumps push any fraud-or-harm offense against a government or critical-infrastructure computer to at least a second-degree felony under (b-2)(6)(B), and even simple no-fraud access to those systems is a state jail felony under (b)(2). On the other side of the ledger, state-jail cases carry one practical relief valve: under Penal Code § 12.44(a), a judge can punish a state jail felony as a Class A misdemeanor in appropriate cases, which is often the negotiated landing spot for a first-time client in the $2,500–$30,000 band.

Employees who exceed their access

The most common § 33.02 fact pattern in a corporate corridor like North Texas is the departing employee who copies a customer list, pricing model, source code, or deal pipeline. The defense lives in the gap between "had login rights" and "had effective consent."

The single most common § 33.02 fact pattern in a corporate corridor like North Texas is the departing employee. Someone resigns or is terminated, and on the way out copies a customer list, a pricing model, source code, or a deal pipeline they built or worked on. The employer’s IT team documents the export, an incident-response vendor quantifies it, and the file arrives at the district attorney’s office already packaged as a felony. These are the cases where the gap between "had login rights" and "had effective consent" matters most.

The defense lives in the details of authorization. Was access ever actually revoked, or did the company simply forget to deprovision the account? Did any written policy clearly prohibit the specific conduct, or is the State stretching a generic acceptable-use clause? Did the employee believe the materials were partly their own work product? Most importantly, can the State prove the employee knew the access was unauthorized at the moment it happened — the Muhammed and Farris requirement? When credentials stayed live and the policies were vague, that knowledge proof is thin. And when the dispute is really about who owns the data, that is a civil fight between a former employer and a former employee, not a crime — a framing that supports declination, charge reduction, or a restitution-driven resolution. Where the copied material is a protected trade secret rather than money or identity data, the State may add a count of theft of trade secrets under § 31.05, which carries its own elements and its own defenses.

A hypothetical captures the pattern. Suppose a sales manager is let go on a Friday, but the company never disables her single sign-on. Over the weekend she logs in from home and downloads the commission spreadsheet she maintained for three years. Access happened and data left the building — but the termination letter said nothing about system access, the account still worked, and she viewed the spreadsheet as her own work. Those facts aim squarely at the knowledge element the State must prove under Muhammed, and at the consent-scope question the company’s own deprovisioning failure created. This is a hypothetical, not a result, and every case turns on its specific facts — but it shows why the defense starts with consent and knowledge, not with the keystrokes.

How § 33.02 compares to the federal CFAA

The federal Computer Fraud and Abuse Act, 18 U.S.C. § 1030, overlaps with § 33.02 but splits on one decisive point: after Van Buren, misusing access you are allowed to have is not a federal crime — yet it can still be charged under Texas law.

The federal Computer Fraud and Abuse Act, 18 U.S.C. § 1030, covers overlapping conduct but splits from Texas law on one decisive point: misuse of access you are allowed to have. In Van Buren v. United States, 593 U.S. 374 (2021), the Supreme Court adopted a "gates-up-or-down" reading of the CFAA — a person "exceeds authorized access" only by entering areas of a computer that are off-limits to him, not by accessing information he is entitled to reach for an improper reason. Under that reading, misusing authorized access is not a federal CFAA crime.

Texas law is built the other way. Section 33.01(12)(E) strips consent that is "used for a purpose other than that for which the consent was given," and § 33.02(b-1)(2) expressly reaches access in violation of a written prohibition or contract when paired with fraud-or-harm intent. The result: conduct that no longer supports a CFAA charge after Van Buren can still be charged under § 33.02 in a Texas courthouse. Forum also changes the stakes. Intrusions touching interstate systems, financial institutions, or federal agencies can draw a federal indictment in the Northern or Eastern District of Texas, where loss under the federal sentencing guidelines — not the § 33.02(b-2) bands — drives exposure. The same conduct can be prosecuted in both systems, and § 33.02(d) separately lets Texas prosecutors charge § 33.02 alongside any other Penal Code section the same conduct violates.

Where these cases are heard in DFW

L and L Law Group defends § 33.02 cases across the four core DFW counties from our Frisco office. Where a case is heard — Collin, Dallas, Denton, or Tarrant — shapes how it moves and where the highest-leverage window falls.

L and L Law Group defends § 33.02 cases across the four core DFW counties from our Frisco office. Where a case is heard shapes how it moves.

Collin County. Misdemeanor § 33.02(a) cases are filed in the county courts at law and felonies in the district courts, all sitting at the Collin County Courthouse at 2100 Bloomdale Road in McKinney. The Frisco–Plano–Allen corporate corridor makes employer-referral cases common here: a company’s IT department documents the intrusion, an incident-response firm quantifies it, and the file lands pre-packaged.

Dallas County. Felony computer-crime cases are heard in the district courts at the Frank Crowley Courts Building and typically move alongside the white-collar docket; misdemeanors run through the county criminal courts. Cases referred by banks, hospital systems, and universities tend to arrive with extensive civil-side forensic work already done.

Denton County. Cases are heard at the Denton County Courts Building in Denton, where family-dispute and small-business fact patterns recur, and outcomes often track how cleanly the consent story can be told on paper.

Tarrant County. Filings run through the Tim Curry Criminal Justice Center in Fort Worth — misdemeanors in the county criminal courts, felonies in the district courts. As elsewhere, early defense contact with the assigned prosecutor, before grand-jury presentment on felony tracks, is frequently the highest-leverage window.

Most § 33.02 cases are investigation-first. By the time an arrest happens, a detective has often had the forensic report, the IT affidavit, and a search-warrant return for weeks. Some clients first learn of the case when officers arrive with a device warrant; others get a phone call inviting them "to give their side." Decline that interview until counsel is present — statements about passwords, permissions, and purposes are exactly what the knowledge element gets built from. After arrest and magistration under CCP art. 15.17, expect bond conditions that can include no-contact orders covering a former employer and sometimes computer- or internet-use restrictions — conditions that can be negotiated and modified, which is critical for clients who work in IT or security. Under the Michael Morton Act, CCP art. 39.14, the defense obtains the State’s file — including forensic images and examiner notes — which an independent expert should re-examine rather than accept.

Enhancements and collateral consequences

Beyond the grading bumps, two prior Chapter 33 convictions make even simple access a state jail felony, and § 33.02(d) lets the State stack charges. For a charge that often starts as workplace friction, the collateral fallout — firearm rights, professional licensing, immigration — is heavy.

Beyond the grading bumps in the table, two prior Chapter 33 convictions make even simple access a state jail felony, and § 33.02(d) lets the State prosecute the same conduct under § 33.02 and any other applicable section — theft, fraudulent use of identifying information under § 32.51, or tampering with a governmental record among them. Victims also hold a parallel civil claim: Civil Practice and Remedies Code Chapter 143 authorizes a damages suit for harmful access by computer, so a criminal file is frequently shadowed by a civil one.

For a charge that often starts as workplace friction, the collateral fallout is heavy. A felony conviction forfeits firearm rights under Penal Code § 46.04 and 18 U.S.C. § 922(g). Any conviction carrying fraud-type intent invites professional-license scrutiny and is poison for careers in IT, security, finance, and healthcare — the very fields where background checks flag computer-misuse offenses. Security clearances, employment in regulated industries, and immigration status (fraud-intent offenses raise moral-turpitude questions that need case-specific analysis) can all be affected. Those consequences, more than the jail range, usually drive defense strategy in a first-offense case — which is why charge posture early matters. A dismissal or acquittal generally supports expunction under CCP Chapter 55A, and completed deferred adjudication usually supports an order of nondisclosure, while a final conviction generally stays on the record for good.
Defense Strategy

What we evaluate first

A handful of defense levers do most of the work in Texas § 33.02 cases. We evaluate every one before charting a path — the knowledge element first, then consent scope, the statutory defenses, attribution, the device-search suppression, and the aggregate-loss audit together set the strategy.

  1. No knowledge that consent was absent
    The Muhammed/Farris rule requires proof the accused knew the access was unauthorized at the moment it happened. In Muhammed v. State, 331 S.W.3d 187, 192 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d), the court held the "knowing" mental state attaches to the consent, not just the act; Farris v. State, No. 10-21-00204-CR (Tex. App.—Waco Feb. 15, 2023, no pet.), applied it to acquit. Shared passwords, never-revoked credentials, joint family accounts, and vague workplace policies all generate reasonable doubt on this element.
  2. Effective consent existed — the scope fight under § 33.01(12)
    Permission from anyone legally authorized to act for the owner is a complete answer. The real battle is scope — what was authorized, by whom, and for how long — and it is fought on documents, not memory. A broad or generous original grant defeats the State’s § 33.01(12)(E) "different purpose" theory because there is no second purpose to point to. Onboarding paperwork, IT provisioning logs, acceptable-use policies, prior practice, and the messages exchanged when access was granted are the defense exhibits.
  3. The security-assessment defense under § 33.02(f)
    Section 33.02(f) protects penetration testers and security contractors whose conduct consisted solely of action taken under a contract with the owner to assess the security of the computer, network, or system or to provide other security-related services. The signed scope-of-work and authorization letter are the central exhibits for security professionals. Section 33.02(e) supplies a parallel lawful-purpose defense for a person acting to facilitate a lawful seizure, search, or access for a legitimate law-enforcement purpose.
  4. Attribution failure
    An IP address identifies a connection, not a person. Shared terminals, open networks, spoofed or stolen credentials, and compromised accounts can all break the link between a login and the accused. Where the State’s proof rests on logs that point to an account or device rather than to the defendant’s hands on the keyboard, the defense develops the alternative-access record and contests the inference that the accused was the actor.
  5. Suppression of the device search under CCP art. 38.23
    Digital searches must satisfy the Fourth Amendment and Texas’s statutory exclusionary rule, Code of Criminal Procedure art. 38.23. An overbroad phone or laptop warrant, or a warrantless account search, can remove the forensic centerpiece from the case entirely. Because § 33.02 prosecutions are built almost entirely on digital evidence, a successful suppression motion can be dispositive.
  6. Attacking the loss number
    Because the felony grade follows the aggregate amount under § 33.01(2), contesting inflated investigation and restoration figures — line by line, against the vendor invoices — can knock a third-degree felony down to a state jail felony or a misdemeanor. The "aggregate amount" sweeps in the victim’s cost to investigate the intrusion and to restore, recover, or replace data, and those forensic-response invoices are frequently padded, duplicative, or untethered to the charged conduct.
  7. Civil dispute dressed as a crime
    Business divorces, partnership feuds, and contractor disputes belong in civil court. When the real fight is who owns the data — not whether a crime occurred — establishing that framing supports declination, charge reduction, or a restitution-driven resolution. Civil Practice and Remedies Code Chapter 143 already gives the complainant a damages remedy, which underscores that the dispute is properly civil rather than criminal.
Defense Timeline

How we build the case

Texas § 33.02 defense follows a predictable four-phase arc — stabilize and preserve the consent record (0-14 days), discovery and forensic re-examination (14-60 days), suppression and loss-amount motion practice (2-6 months), then trial readiness or resolution (6 months+).

  1. Day 0-14
    Arrest or contact, counsel, evidence preservation
    Retain experienced defense counsel before any custodial interview or "give your side" call; invoke the Fifth Amendment and right to counsel; preserve every record that shows what access was authorized and why — emails, onboarding documents, IT provisioning logs, company policy, and text messages; do not delete messages, wipe a device, or "clean up" an account, which can create separate tampering exposure; prepare bond posture and the first court appearance under CCP art. 15.17.
  2. Day 14-60
    Discovery, forensic re-examination, theory development
    Michael Morton Act discovery under CCP art. 39.14, including forensic images and examiner notes; independent re-examination of the State’s forensic work rather than acceptance of it; consent-scope investigation and authorization-document collection; attribution analysis (shared terminals, credentials, account compromise); preliminary aggregate-loss audit against the vendor invoices; assessment of the state-versus-federal forum question.
  3. Month 2-6
    Suppression, loss-amount motions, and plea negotiation
    Motion to suppress the device or account search where the warrant was overbroad or the search warrantless, under CCP art. 38.23; loss-amount challenge to drop the felony grade; consent-scope and knowledge arguments aimed at declination or reduction; pre-indictment contact with the prosecutor on felony tracks; plea negotiation including § 12.44(a) misdemeanor-range punishment for a state jail felony, deferred adjudication, and pretrial diversion for first-time clients.
  4. Month 6+
    Trial readiness or resolution
    Trial settings typically 6-12 months from charging in DFW courts. A bench or jury trial proceeds with the State required to prove knowing access, absence of effective consent, and knowledge that consent was absent — plus fraud-or-harm intent and the aggregate amount on felony tracks — through forensic and fact witnesses; jury instructions on the knowledge element and any statutory defense; record-relief planning so that a dismissal or acquittal supports expunction under CCP Chapter 55A and completed deferred adjudication supports an order of nondisclosure.

Charged with breach of computer security in Collin, Dallas, Denton, or Tarrant County?

L and L Law Group defends § 33.02 cases at every level — Class B misdemeanor through first-degree felony, in state and federal court. Free initial consultation.

Call (972) 370-5060

Frequently asked questions

Nine questions we answer most often about Texas breach of computer security cases — the knowledge element, shared passwords, felony grading, the loss number, fired-employee access, the security-assessment defense, state versus federal court, Van Buren, and record relief.

Does the State have to prove I knew I did not have permission?

Yes. The knowing mental state under § 33.02 reaches both the access and the consent. In Muhammed v. State, 331 S.W.3d 187, 192 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d), the court held the State must prove the defendant knowingly accessed the computer knowing that the access was without the owner’s effective consent. That second knowledge requirement is where shared-password and workplace cases are most often won.

Can I be charged for logging into an account when I had the password?

Yes — possessing valid credentials is not the same as having the owner’s effective consent. Under § 33.01(12)(E), consent does not count if it is used for a purpose other than the one for which it was given. A password shared for paying bills does not authorize using it to gather evidence in a divorce. The State must still prove you knew the access was unauthorized.

Is breach of computer security a felony in Texas?

It can be either. Simple unauthorized access under § 33.02(a) is a Class B misdemeanor. It becomes a state jail felony if the target is a government or critical-infrastructure computer or the defendant has two or more prior Chapter 33 convictions. Access with intent to defraud or harm is graded by aggregate amount and can reach a first-degree felony.

How does the aggregate amount drive the felony grade?

On the fraud-or-harm track, § 33.02(b-2) grades the offense by the aggregate amount involved. Under § 33.01(2) that figure sweeps in the victim’s cost to investigate the intrusion and to restore, recover, or replace data — often a forensic-response invoice. Because that number sets the grade, auditing it line by line can drop a third-degree felony to a state jail felony or a misdemeanor.

Can a former employee be charged for accessing a work system after being fired?

It happens often, but the charge turns on consent and knowledge. If credentials were never revoked and the termination paperwork said nothing about system access, whether consent ended — and whether the employee knew it ended — becomes the contested issue. Section 33.02(b-1)(2) can reach an authorized user who violates a clear written policy, but only with proof of intent to defraud or harm.

What is the security-assessment defense for penetration testers?

Section 33.02(f) is a defense to a (b-1)(2) prosecution when the actor’s conduct consisted solely of action taken under a contract with the owner to assess the security of the computer, network, or system or to provide other security-related services. The signed scope-of-work and authorization letter are the central exhibits for security professionals.

Will my case be filed in state or federal court?

Both are possible. Texas prosecutors file § 33.02 cases in Collin, Dallas, Denton, and Tarrant County courts. Intrusions touching interstate systems, financial institutions, or federal agencies can be charged under the federal Computer Fraud and Abuse Act, 18 U.S.C. § 1030, in the Northern or Eastern District of Texas. The same conduct can support charges in both systems.

Does the federal Van Buren decision help a Texas § 33.02 case?

Not directly. Van Buren v. United States, 593 U.S. 374 (2021), narrowed the federal CFAA so that misusing access you are allowed to have is not a federal crime. Texas law is written differently: § 33.01(12)(E) strips consent used for an unauthorized purpose, and § 33.02(b-1)(2) reaches policy violations paired with fraud intent. Conduct that survives Van Buren federally can still be charged under § 33.02 in a Texas courthouse.

Can a breach of computer security charge be dismissed or expunged?

Weak knowledge evidence, consent ambiguity, or suppression exposure can support dismissal or declination, and first-time defendants are often candidates for pretrial diversion or deferred adjudication. A dismissal or acquittal generally supports expunction under Code of Criminal Procedure Chapter 55A; completed deferred adjudication usually supports an order of nondisclosure. A final conviction generally cannot be sealed, which is why charge posture early matters.

References

All citations link to statutes.capitol.texas.gov for primary text. Footnote numbers in the body link here; the ↩ arrow returns to the citing paragraph.

  1. Tex. Penal Code § 33.02 — Breach of computer security. ↩
  2. Tex. Penal Code § 33.01 — Definitions (access, aggregate amount, effective consent). ↩
  3. Muhammed v. State, 331 S.W.3d 187 (Tex. App.—Houston [14th Dist.] 2011, pet. ref’d). ↩
  4. Farris v. State, No. 10-21-00204-CR (Tex. App.—Waco Feb. 15, 2023, no pet.) (mem. op.). ↩
  5. Van Buren v. United States, 593 U.S. 374 (2021); 18 U.S.C. § 1030. ↩
  6. Tex. Penal Code § 12.44 — State jail felony punished as a misdemeanor. ↩
  7. Tex. Code Crim. Proc. art. 38.23 — Exclusionary rule (device and account searches). ↩
  8. Tex. Code Crim. Proc. art. 39.14 — Michael Morton Act discovery. ↩
  9. Tex. Civ. Prac. & Rem. Code ch. 143 — Civil liability for harmful access by computer. ↩
40+
Years
Combined defense experience
$0
Consult
Free initial consultation
24/7
Available
Direct-to-attorney for jail release
About the authors

The attorneys behind this page

Reggie London

Reggie London

Co-Founding Partner · Criminal Defense Attorney

Admitted in Texas, TXND, TXED, and the U.S. Court of Appeals for the Fifth Circuit. Practice spans DWI, drug, weapons, theft, and process crimes — plus federal practice.

Njeri London

Njeri London

Co-Founding Partner · Criminal Defense Attorney

Texas-licensed criminal defense attorney with deep Fourth Amendment motion practice. Focus: suppression hearings, drug-crime defense, federal-practice support.

From the blog

Related writing on this topic

Free Consultation · 24/7

Talk to an attorney — not a screener.

Tell us about your case. Most clients hear back within an hour. Often within minutes.

5899 Preston Rd, Ste 101 · Frisco, TX 75034

By submitting, you agree to our Privacy Policy.

Call (972) 370-5060

Attorney Advertising

This website is for general information purposes only and constitutes attorney advertising under the Texas Disciplinary Rules of Professional Conduct. Nothing on this site should be taken as legal advice for any individual case or situation. Receipt or viewing does not create an attorney–client relationship.

Past results do not guarantee similar outcomes. Each case is unique and must be evaluated on its own facts and circumstances.

L and L Law Group, PLLC attorneys are licensed to practice in the State of Texas. Njeri London (Texas Bar No. 24043266) and Reggie London (Texas Bar No. 24043514) are the attorneys responsible for the content of this site. None of the attorneys at L and L Law Group, PLLC are Board Certified by the Texas Board of Legal Specialization unless specifically and separately stated.

Please do not transmit any confidential information to L and L Law Group, PLLC by email, web form, or telephone before a written engagement is in place. Privacy Policy.

Service Areas

L&L Law Group represents clients across North Texas counties for DWI, assault, drug crimes, juvenile defense, outstanding warrants, bond reduction, and expunction matters.

Call Email Map Top
developed by MPR Digital Legal Services